


Realm creation and authentication flow
A realm manages a set of users, credentials, roles, and groups. Each realm is isolated from one another and can only manage and authenticate the users under their control.
The realm is configured in two ways:
Manual configuration of the realm
Perform the steps below to configure the realm using the SafeNetOTPRealm.json and the SafeNet Access Exchange Admin UI for SAS PCE and STA Hybrid Access Management Add-On based deployment:
-
Log in to the SafeNet Access Exchange Admin UI as an Administrator user (created in Installation).
-
In the left pane, click Create Realm.
-
Browse the required json file, specify the realm name, and click Create.
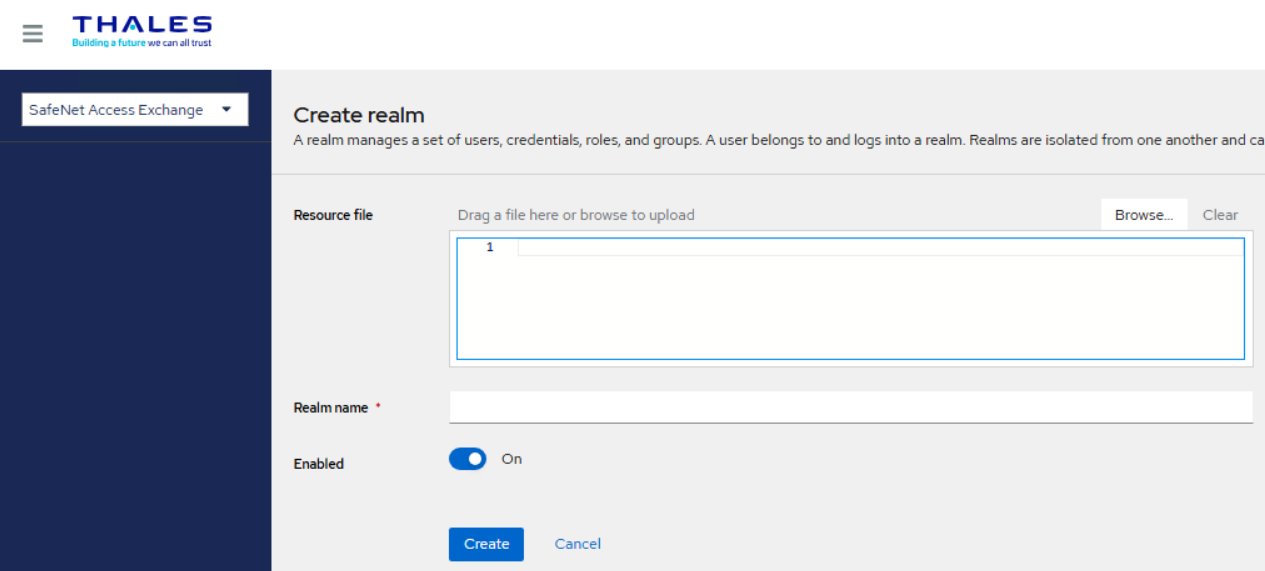
The realm is created with the following SafeNet authentication flows: SafeNet OTP Flow, SafeNet OTP UserId Provided Flow, SafeNet LDAP OTP Flow, SafeNet OTP LDAP Flow, SafeNet LDAP FIDO flow, and SafeNet OTP FIDO flow.
Each SafeNet authentication flow also contains an SAE Risk Score Evaluator step that is set to Disabled. Keep this step disabled and in its current position. To evaluate a risk score stored in LDAP/Active Directory, see Risk Score-Based authentication flows.
-
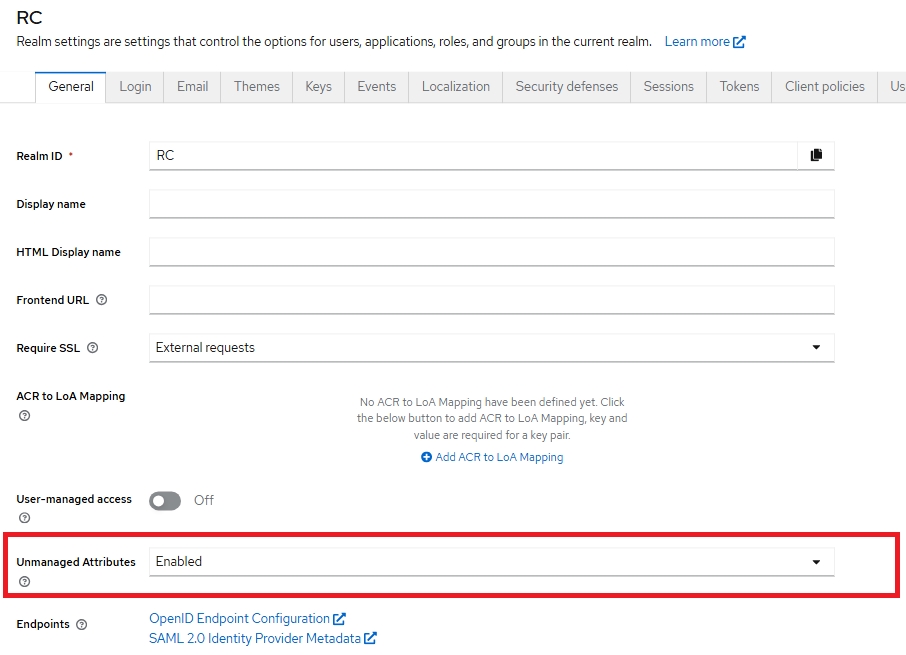
Navigate to Realm settings > General.
-
Enable Unmanaged Attributes.
-
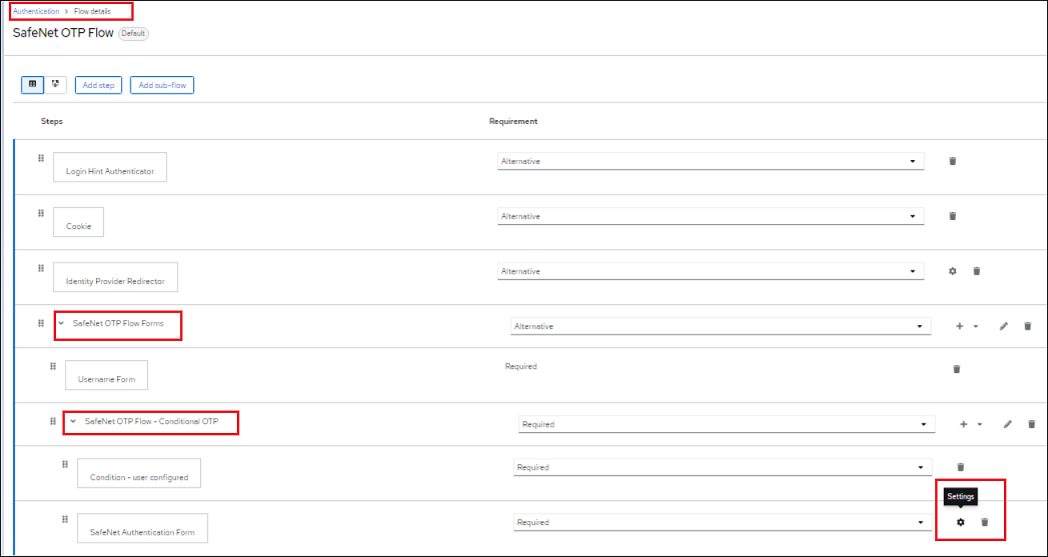
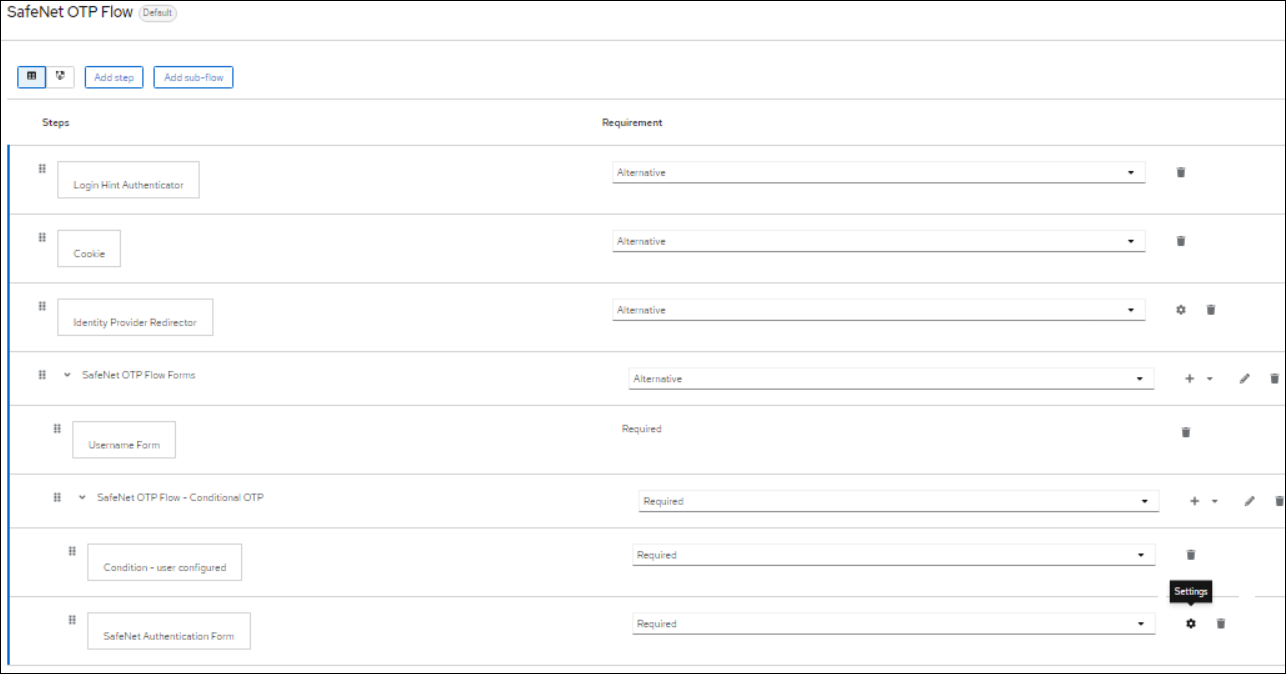
Select the SafeNet OTP Flow and click the Setting icon at the bottom-right of the page, as highlighted in the figure below:
-
A pop-up displays. Enter the details and click Save.
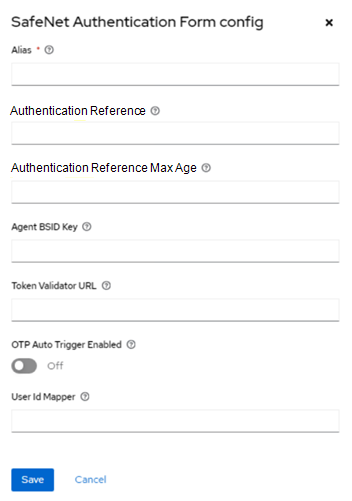
This configuration is required for all SafeNet OTP Authentication flows.
Agent BSID key
Path of Agent.bsidkey file or Content of Agent.bsidkey
-
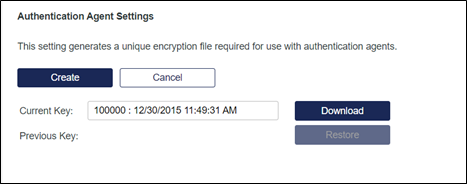
In the SAS console, navigate to the Comms tab in the required Virtual Server to download the Agent BSID Key.
-
Navigate to the Authentication Processing > Authentication Agent Settings. Click Download to download the agent.bsidkey file.
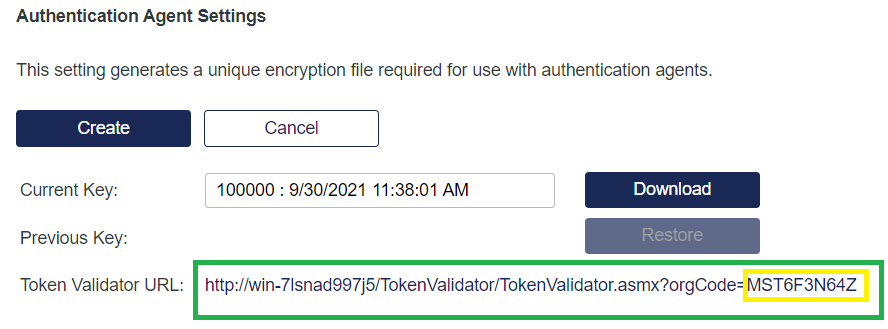
Token Validator URL
http(s)://<sas-ip>:<port>/TokenValidator/TokenValidator.asmx?orgCode=<OrgCode>
-
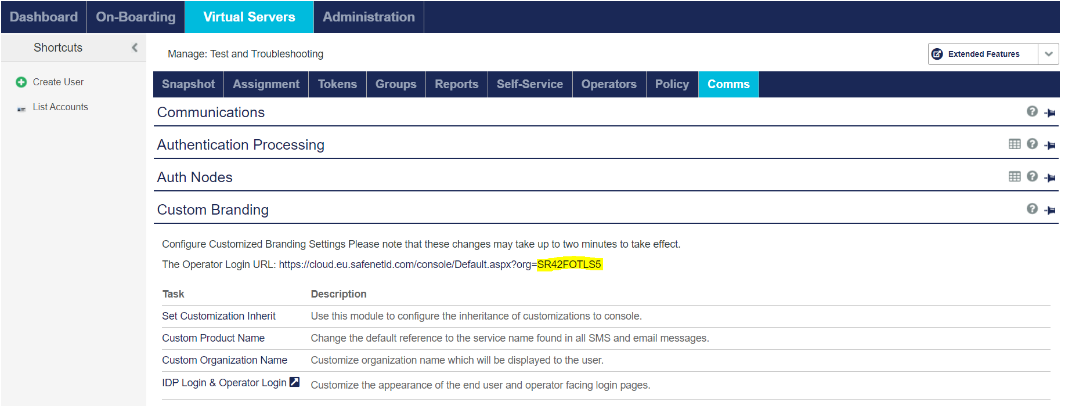
To find OrgCode details, go to the SAS console.
-
Navigate to the Comms tab in the required Virtual Server to get the organization code for the token validator url.
These settings can be found under the Authentication Processing > Authentication Agent Settings.
These settings are only visible on SafeNet Authentication Service PCE v3.13 and above.
OTP Auto Trigger Enabled (optional)
Toggle this setting to enable/disable the auto trigger of OTP. If enabled the challenge automatically generates the enrolled token.
User Id Mapper Field (optional)
This field is used in combination with LDAP User Provider. It is used to send different user attribute as a UserName to SafeNet Authentication Service. The field value is named upon any LDAP Mapper. If the field value is not defined, default UserName from the request is sent to SafeNet Authentication Service.
Configuration with SafeNetOTPRealm.json
Perform the following steps to add configuration values in the json file:
-
Edit SafeNetOtpRealm.json using a text editor.
-
Search for the agent.bsidkey key.
Set the path of the agent.bsidkey file to C:\\Downloads\\agent.bsidkey or content of the agent.bsidkey file: <content-of-agent.bsidkey-file>.For more details, refer to the agent.bsidkey section.
-
Search for tokenvalidator.url key.
Set the value of TokenValidator URL, with organization code. For more details, refer to the Organization Code Details section. tokenvalidator.url:http(s)://<sas-ip>:<port>/TokenValidator/TokenValidator.asmx?orgCode=<OrgCode> -
Search for user.id.mapper key.
Set the value of User Id Mapper with name of defined LDAP Mapper for the required attribute. -
For details, refer to the Custom LDAP Mapper section.
In Windows, while copying the path in json, make sure to use "\\" instead of "\" in the path to adhere to the json syntax. For example, if the path is C:\Agent.bsidkey then use C:\\Agent.bsidkey.
-
-
Log in to the Access Exchange Admin UI as an Administrator user (created in Installation).
Save the SafeNetOTPRealm.json on a different path, other than the package location (recommended).
-
In the left pane, click Create realm.
-
Browse the required json file, specify the realm name, and click Create.
-
Navigate to Realm settings > General.
-
Enable Unmanaged Attributes.
SafeNet authentication flow
SafeNet Access Exchange provides SAS Authentication flow. You can select a flow that works best for you.
Each flow can also evaluate a risk score stored in LDAP/Active Directory and allow, step up, or deny users accordingly. For more information, see Risk Score-Based authentication flows.
SafeNet OTP flow (default flow)
Ideal for the integrations, where password or first factor authentication is done at the Service Provider (or Application) and you just need the second factor OTP authentication at the Access Exchange Identity Provider.
-
Service Provider (or Application) authenticates Password as first factor with its User or Domain password before reaching to Access Exchange.
-
Navigate to User Name form presented by Access Exchange. (User Name is auto-filled, from the request, if available).
-
SafeNet Authentication form presented by Access Exchange authenticates OTP as second factor with SafeNet Authentication Service. (Follow steps from Realm Configuration section).
RiskScore: To allow, step up, or deny users of this flow based on a risk score stored in LDAP/Active Directory, add the SAE Risk Score Evaluator and a Risk Step-Up sub-flow. For more information, see SafeNet OTP Flow with risk score evaluation.
SafeNet OTP userid provided flow
Ideal for the integrations same as “SafeNet OTP Flow” where you wish to skip User Name prompt at the SafeNet Access Exchange. User Name is extracted from the request and browser request navigates to the final OTP prompt page.
-
Service Provider (or Application) authenticates Password as first factor with its User or Domain password before reaching to SafeNet Access Exchange.
-
SafeNet Authentication Form prompted by SafeNet Access Exchange authenticates OTP as second factor with SafeNet Authentication Service. (Follow steps from Realm Configuration section).
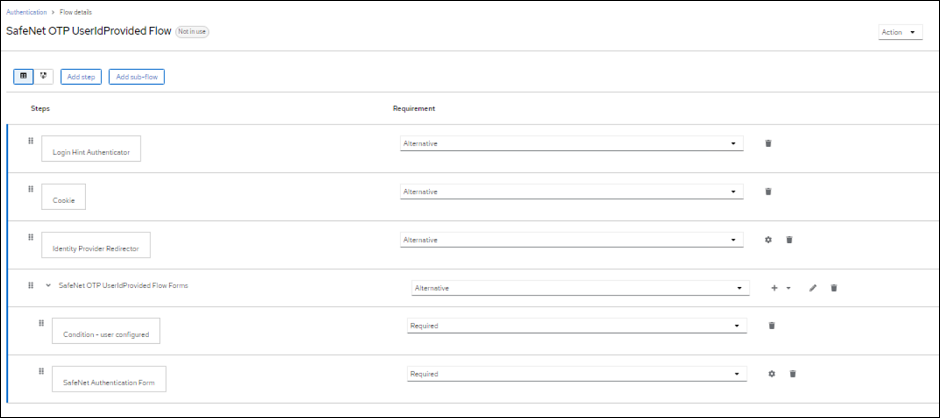
RiskScore: To allow, step up, or deny users of this flow based on a risk score stored in LDAP/Active Directory, add the SAE Risk Score Evaluator and a Risk Step-Up sub-flow. For more information, see SafeNet OTP UserIdProvided Flow with risk score evaluation.
SafeNet LDAP OTP flow
Ideal for the integrations where you want to handle the 2FA (Password + OTP) at the SafeNet Access Exchange Identity Provider.
-
SafeNet Access Exchange LDAP User Federation provider authenticates Password as first factor with Domain password.
-
SafeNet Authentication Form prompted by SafeNet Access Exchange authenticates OTP as second factor with SafeNet Authentication Service. (Follow steps from Realm Configuration section).
-
If you are using an existing realm, you must add an "LDAP Session Details Authenticator" after "Username Password Form", on the same level.
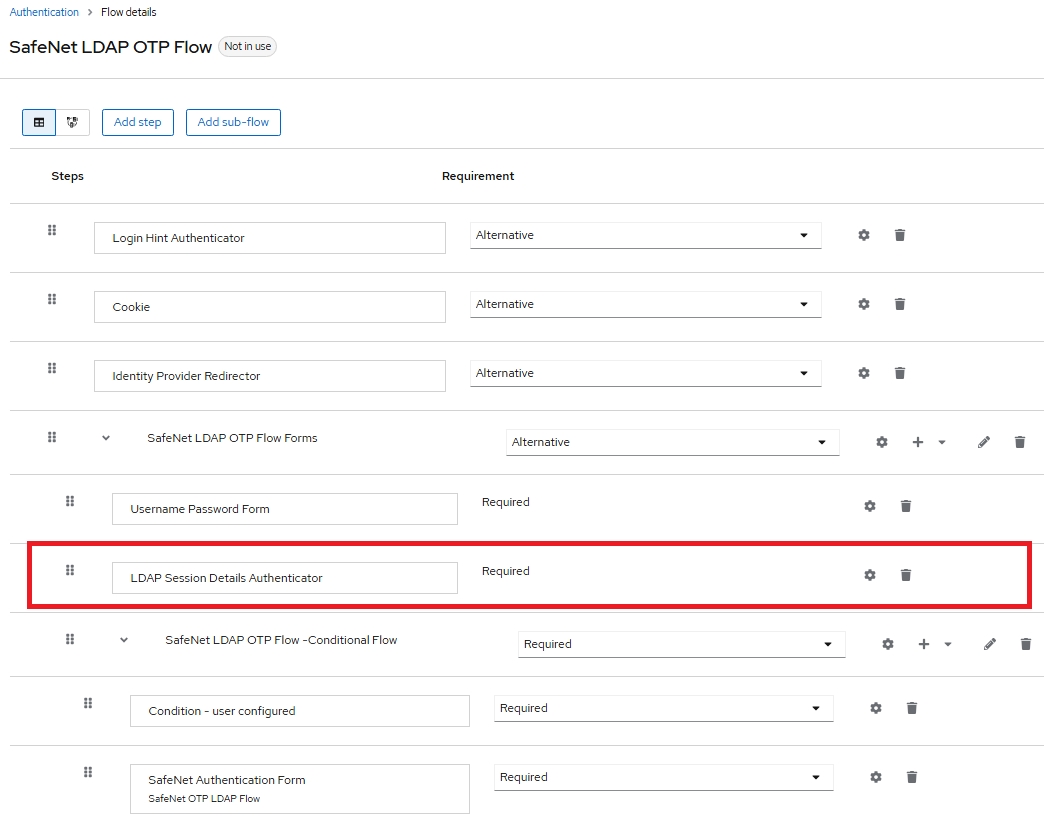
RiskScore: To allow, step up, or deny users of this flow based on a risk score stored in LDAP/Active Directory, add the SAE Risk Score Evaluator and a Risk Step-Up sub-flow. For more information, see SafeNet LDAP OTP Flow with risk score evaluation.
SafeNet OTP LDAP flow
Ideal for the integrations where you want to handle the 2FA (OTP + Password ) at the SafeNet Access Exchange Identity Provider.
-
SafeNet Authentication Form prompted by SafeNet Access Exchange authenticates the OTP as first factor with SafeNet Authentication Service. (Follow the steps from Realm Configuration section).
-
SafeNet Access Exchange LDAP User Federation provider authenticates password as second factor with Domain password.
-
If you are using an existing realm, you must add an "LDAP Session Details Authenticator" after "Username Password Form", on the same level.
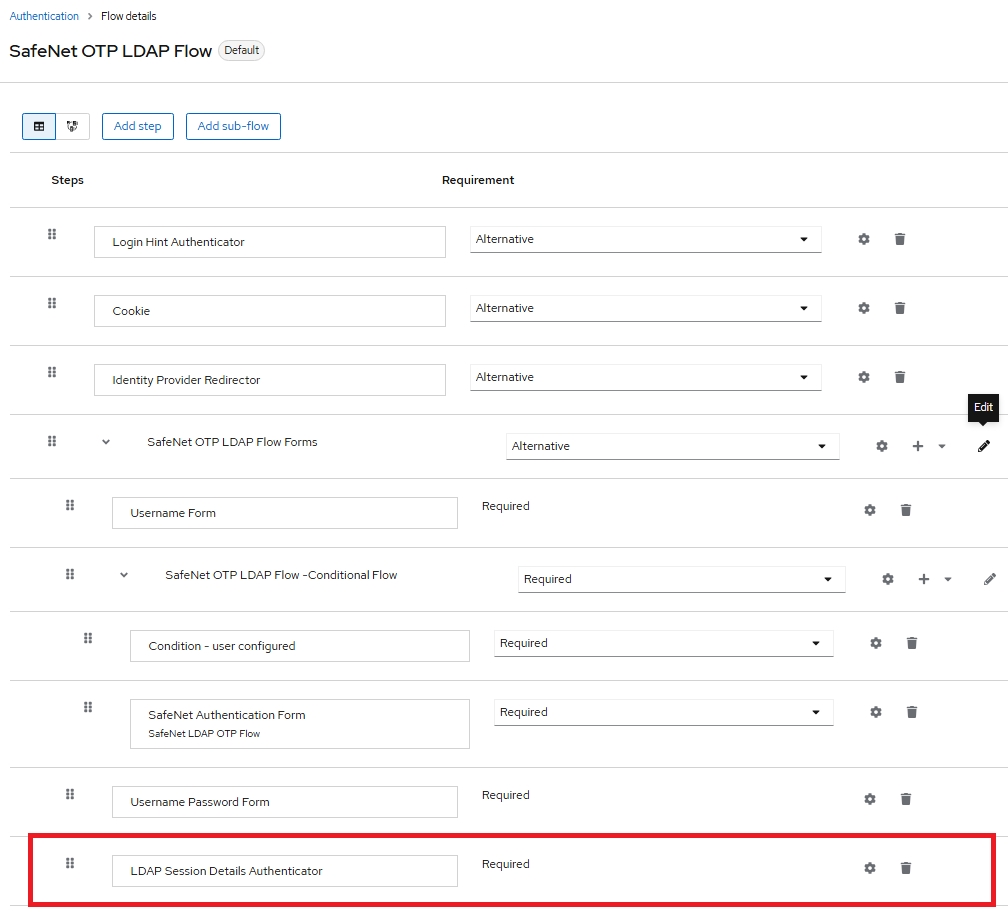
For existing realms, a new workflow for SafeNet OTP LDAP Flow can be added by following the below steps:
-
Log in to SafeNet Access Exchange Admin console.
-
In the left pane, select your desired realm.
-
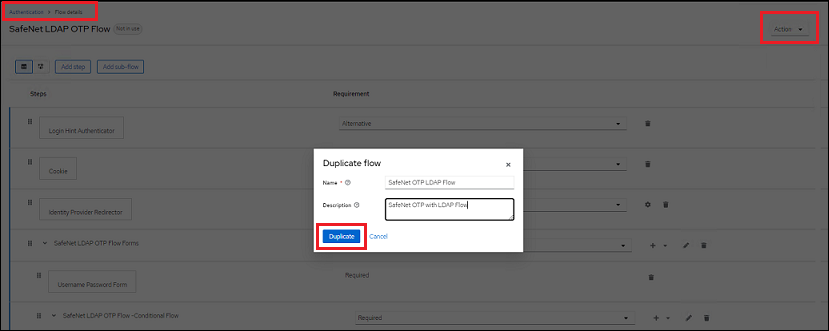
In the left pane, click Authentication and under the Flows tab, select the SafeNet LDAP OTP Flow.
-
From the Action drop-down, select Duplicate to copy the flow.
-
In the Duplicate Flow window, enter the relevant details and click Duplicate.
-
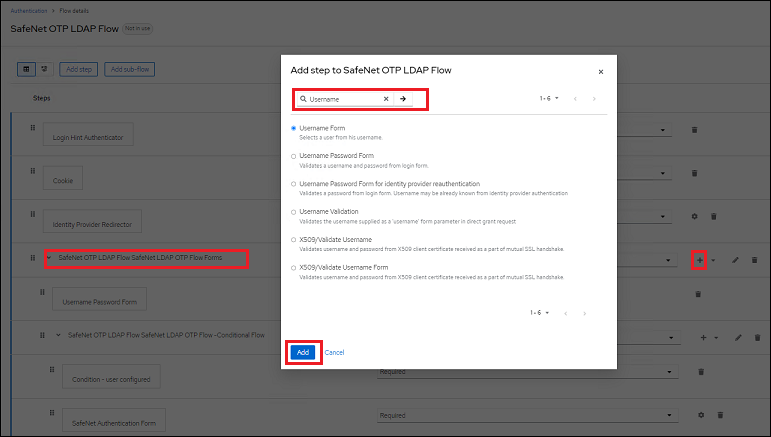
In the Authentication Flow details, ensure SafeNet OTP LDAP Flow is selected, click the Add icon.
The Add step to SafeNet OTP LDAP Flow pop-up window is displayed.
-
Search for the Username Form, select it from the provided options, and click Add.
-
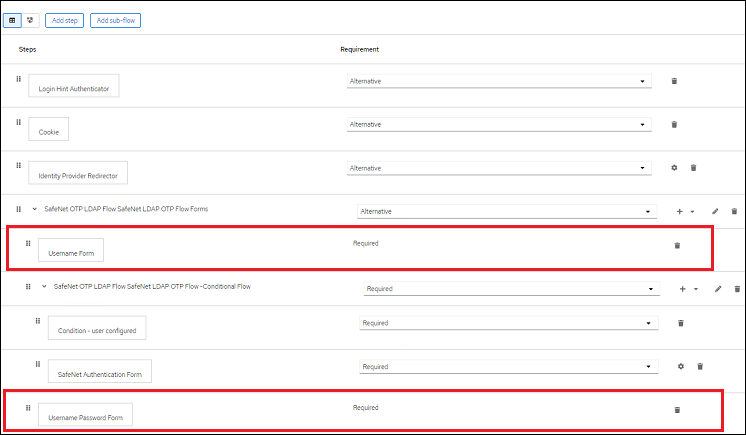
Now, manually rearrange /move the Username Form and Username Password Form in the order as shown below:
RiskScore: To allow, step up, or deny users of this flow based on a risk score stored in LDAP/Active Directory, add the SAE Risk Score Evaluator and a Risk Step-Up sub-flow. For more information, see SafeNet OTP LDAP Flow with risk score evaluation.
SafeNet LDAP FIDO flow
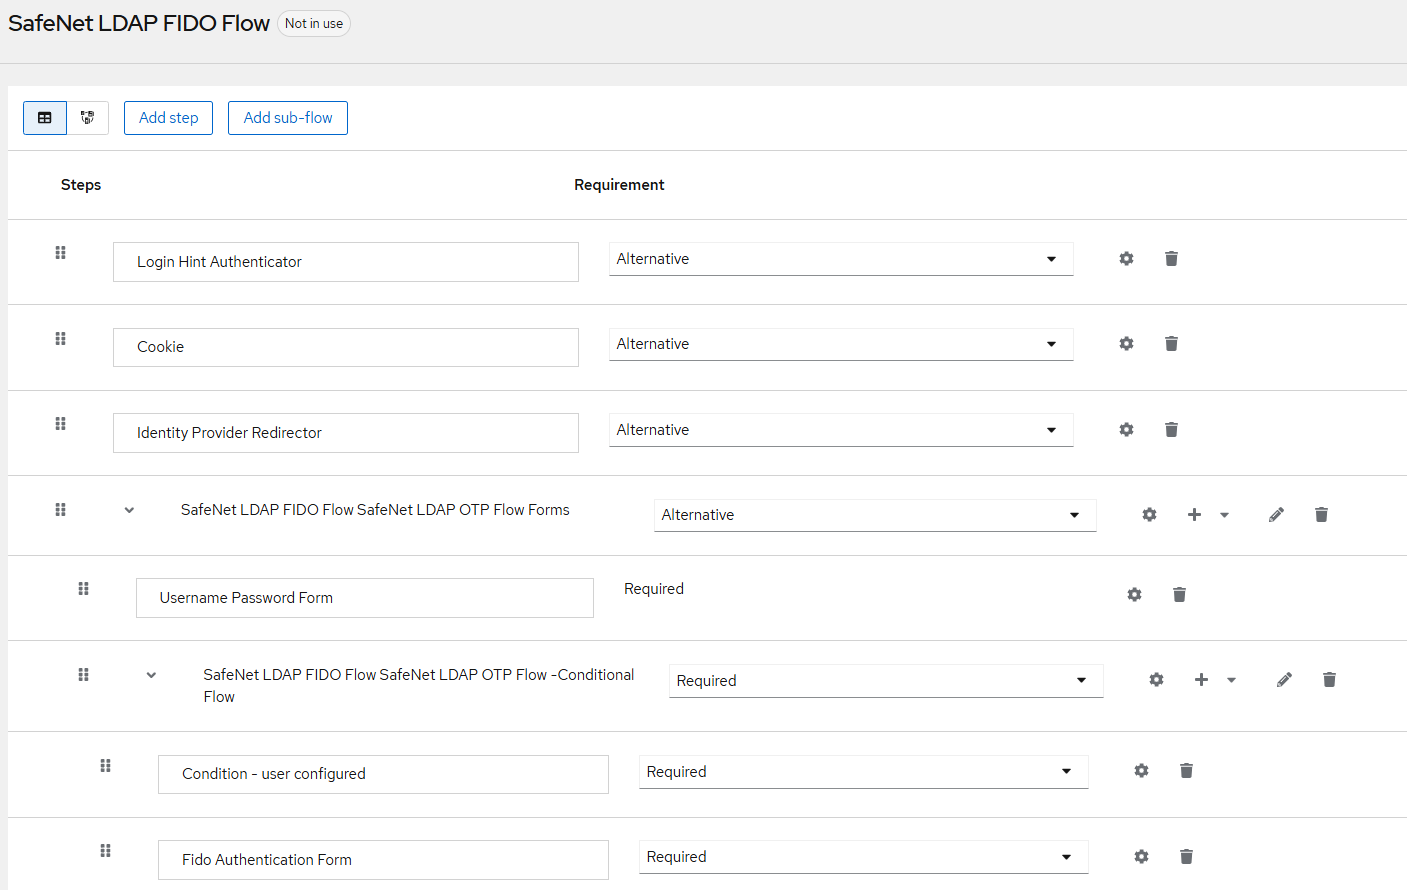
Use Case: Handling 2FA (Domain password + FIDO) integrations managed at the SafeNet Access Exchange Identity Provider
-
The SafeNet Access Exchange LDAP User Federation Provider authenticates Password as the first factor with Domain password.
-
The SafeNet Authentication Form, prompted by the SafeNet Access Exchange, authenticates FIDO as the second factor using the SafeNet Authentication Service. Refer to the Realm Configuration section for detailed steps.
-
For existing realms, ensure to add the LDAP Session Details Authenticator immediately after the Username Password Form at the same level within the authentication flow.
Note
It is not recommended to use FIDO as the first or only authentication factor due to security concerns. It is strongly advised to use another authentication method—such as OTP or LDAP—to pre-authenticate users prior to FIDO enrollment.
RiskScore: To allow, step up, or deny users of this flow based on a risk score stored in LDAP/Active Directory, add the SAE Risk Score Evaluator and a Risk Step-Up sub-flow. For more information, see SafeNet LDAP FIDO Flow with risk score evaluation.
SafeNet OTP FIDO flow
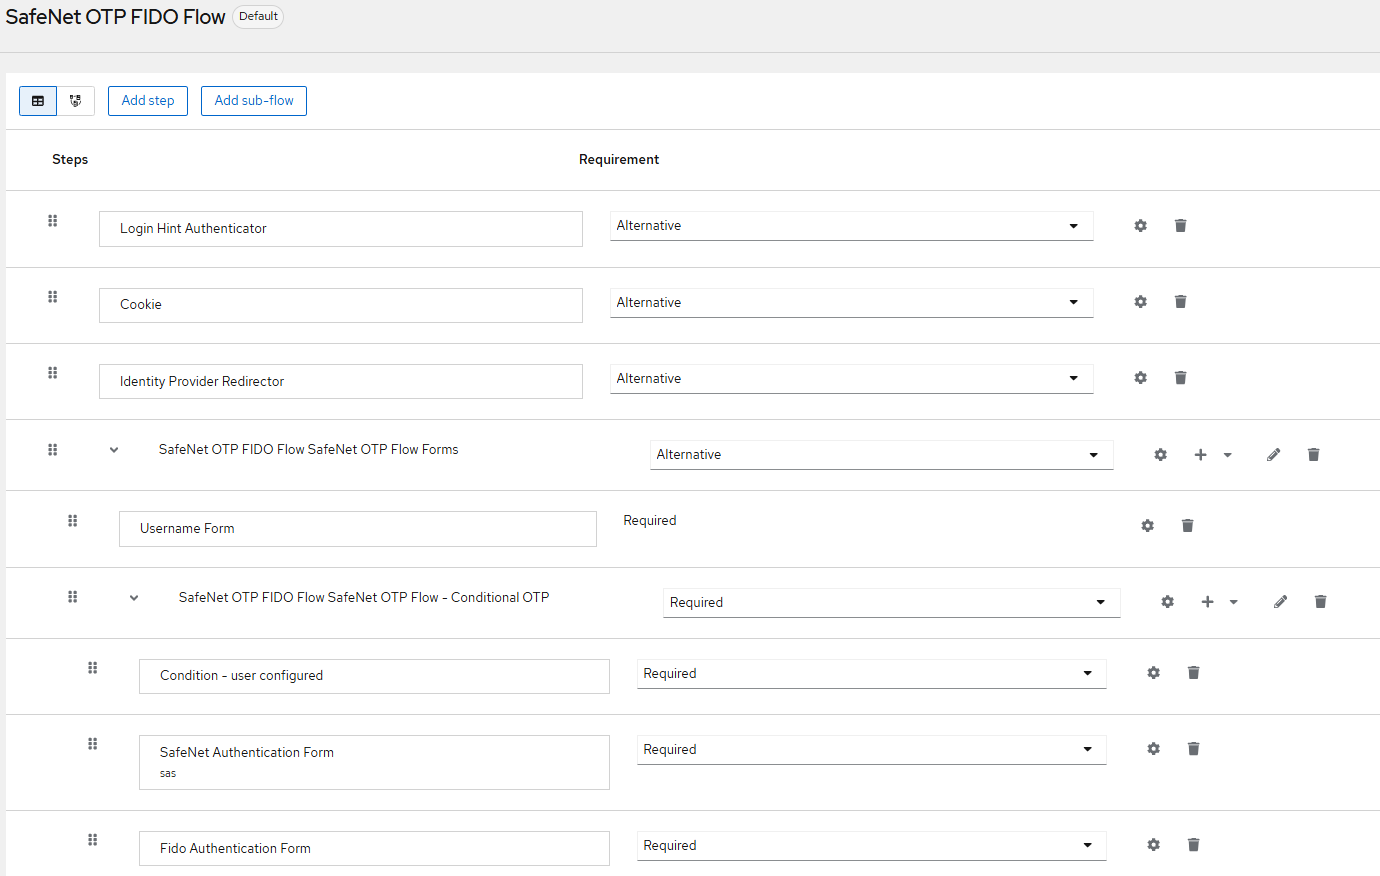
Use Case: Handling 2FA (OTP + FIDO) integrations managed at the SafeNet Access Exchange Identity Provider
-
The SafeNet Authentication Form, prompted by the SafeNet Access Exchange, authenticates OTP as the first factor using the SafeNet Authentication Service. Refer to the Realm Configuration section for detailed steps.
-
The SafeNet Authentication Form then authenticates FIDO as the second factor.
-
For existing realms, ensure to add the FIDO Authentication Form immediately after the SafeNet Authentication Form at the same level within the authentication flow. Also, add FIDO Authentication Form after the Condition – user configured at the same level.
Note
It is not recommended to use FIDO as the first or only authentication factor due to security concerns. It is strongly advised to use another authentication method—such as OTP or LDAP—to pre-authenticate users prior to FIDO enrollment.
RiskScore: To allow, step up, or deny users of this flow based on a risk score stored in LDAP/Active Directory, add the SAE Risk Score Evaluator and a Risk Step-Up sub-flow. For more information, see SafeNet OTP FIDO Flow with risk score evaluation.
Configure FIDO authentication flow for existing Realms
To add a new workflow for the SafeNet OTP FIDO Flow in an existing realm, perform the following steps:
-
Log in to the SafeNet Access Exchange Admin Console.
-
In the left pane, select the desired realm.
-
Click Authentication, go to the Flows tab, and then select the SafeNet OTP Flow.
-
From the Action drop-down, select Duplicate to create a copy of the flow.
-
In the Duplicate Flow window, enter the relevant details and click Duplicate.
-
Open the newly duplicated flow and under the Conditional OTP section, add a new step FIDO Authentication Form, as shown in the screenshots below.
-
Set the newly added FIDO Authentication Form step as Required by selecting Required from the Requirement drop-down.
Note
Similarly, users can duplicate the SafeNet LDAP Flow to create a customized SafeNet LDAP FIDO Flow. These flows can be tailored as needed based on specific authentication requirements.
Default authentication flow changes for realm
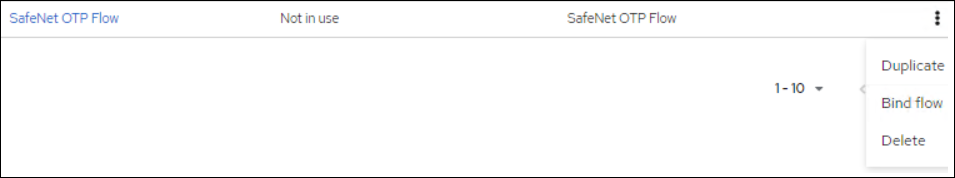
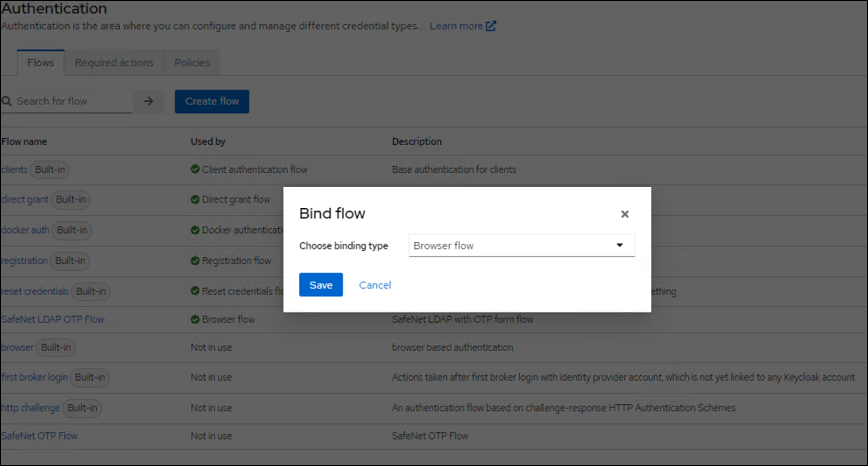
Note
When Custom Federation is configured with SAS User Federation, the LDAP Authentication only works in case the user is synched using Safenet Authentication Service Synchronization Agent with Enable Password Synchronization enabled.
Risk Score-Based authentication flows
Any SafeNet authentication flow can evaluate a risk score published to LDAP/Active Directory (for example, by SailPoint IdentityIQ) and mapped to an SAE user attribute. After identifying the user, the SAE Risk Score Evaluator reads the risk score and applies the outcome configured for the corresponding risk band:
| Risk band | Default outcome | Result |
|---|---|---|
| LOW | ALLOW | The user is signed in. |
| MEDIUM | STEP_UP | The user must complete an additional authentication factor in the Step-Up sub-flow. |
| HIGH | DENY | The user is denied access. |
| No score | — | The user is signed in, as with the standard SafeNet flow. |
For prerequisites, LDAP mapper, evaluator settings, and testing, see Risk Score-Based Authentication Flows.
SAE Risk Score Evaluator in new and existing realms
| Realm | SAE Risk Score Evaluator in the SafeNet flows | What to do |
|---|---|---|
New realm, created from the SafeNetOtpRealm.json file delivered with SafeNet Access Exchange 2.0 |
Present at the bottom of each flow and set to Disabled | Delete the step at the bottom of the flow, add the evaluator inside the Forms sub-flow and add a Step-Up sub-flow. |
Existing realm, created from the SafeNetOtpRealm.json file of an earlier release |
Not present | Add the evaluator inside the Forms sub-flow and add a Step-Up sub-flow. |
For step-by-step instructions, see Identity Provider (SafeNet Access Exchange) Setup.
Do not change the SAE Risk Score Evaluator step at the bottom of a SafeNet authentication flow from Disabled to Required in its delivered position. At that level, it runs alongside the Cookie, Identity Provider Redirector, and sign-in form steps. As a result, SafeNet Access Exchange skips those steps, and all sign-ins fail.
Structure of a SafeNet flow with risk score evaluation
Two additions are made inside the Forms sub-flow of the SafeNet flow, after the steps that identify and authenticate the user:
| Addition | Requirement | Contents |
|---|---|---|
| SAE Risk Score Evaluator | Required | Evaluates the risk score. |
| Risk Step-Up (sub-flow) | Conditional | Condition - SAE Risk Score Step-Up (Required) and the step-up factor (Required). |
The step-up factor can be any authenticator that the user has not already completed in the flow:
| SafeNet flow | Step-up factor examples |
|---|---|
| SafeNet OTP Flow, SafeNet OTP UserIdProvided Flow | Password Form (domain password), FIDO Authentication Form or certificate-based authentication |
| SafeNet LDAP OTP Flow, SafeNet OTP LDAP Flow | FIDO Authentication Form or certificate-based authentication |
| SafeNet LDAP FIDO Flow | SafeNet Authentication Form (OTP) or certificate-based authentication |
| SafeNet OTP FIDO Flow | Password Form (domain password) or certificate-based authentication |
The following examples use one step-up factor for each flow.
SafeNet OTP Flow with risk score evaluation
SafeNet OTP Flow
├── Login Hint Authenticator                      Alternative
├── Cookie                                        Alternative
├── Identity Provider Redirector                  Alternative
└── SafeNet OTP Flow Forms                        Alternative  (sub-flow)
    ├── Username Form                             Required
    ├── SafeNet OTP Flow - Conditional OTP        Required     (sub-flow)
    │   ├── Condition - user configured           Required
    │   └── SafeNet Authentication Form           Required
    ├── SAE Risk Score Evaluator                  Required
    └── SafeNet OTP Flow Risk Step-Up             Conditional  (sub-flow)
        ├── Condition - SAE Risk Score Step-Up    Required
        └── Password Form                         Required
SafeNet OTP UserIdProvided Flow with risk score evaluation
The user name is taken from the request. The SAE Risk Score Evaluator is placed after the step that identifies the user.
SafeNet OTP UserIdProvided Flow
├── Login Hint Authenticator                      Alternative
├── Cookie                                        Alternative
├── Identity Provider Redirector                  Alternative
└── SafeNet OTP UserIdProvided Flow Forms         Alternative  (sub-flow)
    ├── Condition - user configured               Required
    ├── SafeNet Authentication Form               Required
    ├── SAE Risk Score Evaluator                  Required
    └── SafeNet OTP UserIdProvided Flow Risk Step-Up   Conditional  (sub-flow)
        ├── Condition - SAE Risk Score Step-Up    Required
        └── Password Form                         Required
SafeNet LDAP OTP Flow with risk score evaluation
SafeNet LDAP OTP Flow
├── Login Hint Authenticator                      Alternative
├── Cookie                                        Alternative
├── Identity Provider Redirector                  Alternative
└── SafeNet LDAP OTP Flow Forms                   Alternative  (sub-flow)
    ├── Username Password Form                    Required
    ├── LDAP Session Details Authenticator        Required
    ├── SafeNet LDAP OTP Flow -Conditional Flow   Required     (sub-flow)
    │   ├── Condition - user configured           Required
    │   └── SafeNet Authentication Form           Required
    ├── SAE Risk Score Evaluator                  Required
    └── SafeNet LDAP OTP Flow Risk Step-Up        Conditional  (sub-flow)
        ├── Condition - SAE Risk Score Step-Up    Required
        └── FIDO Authentication Form              Required
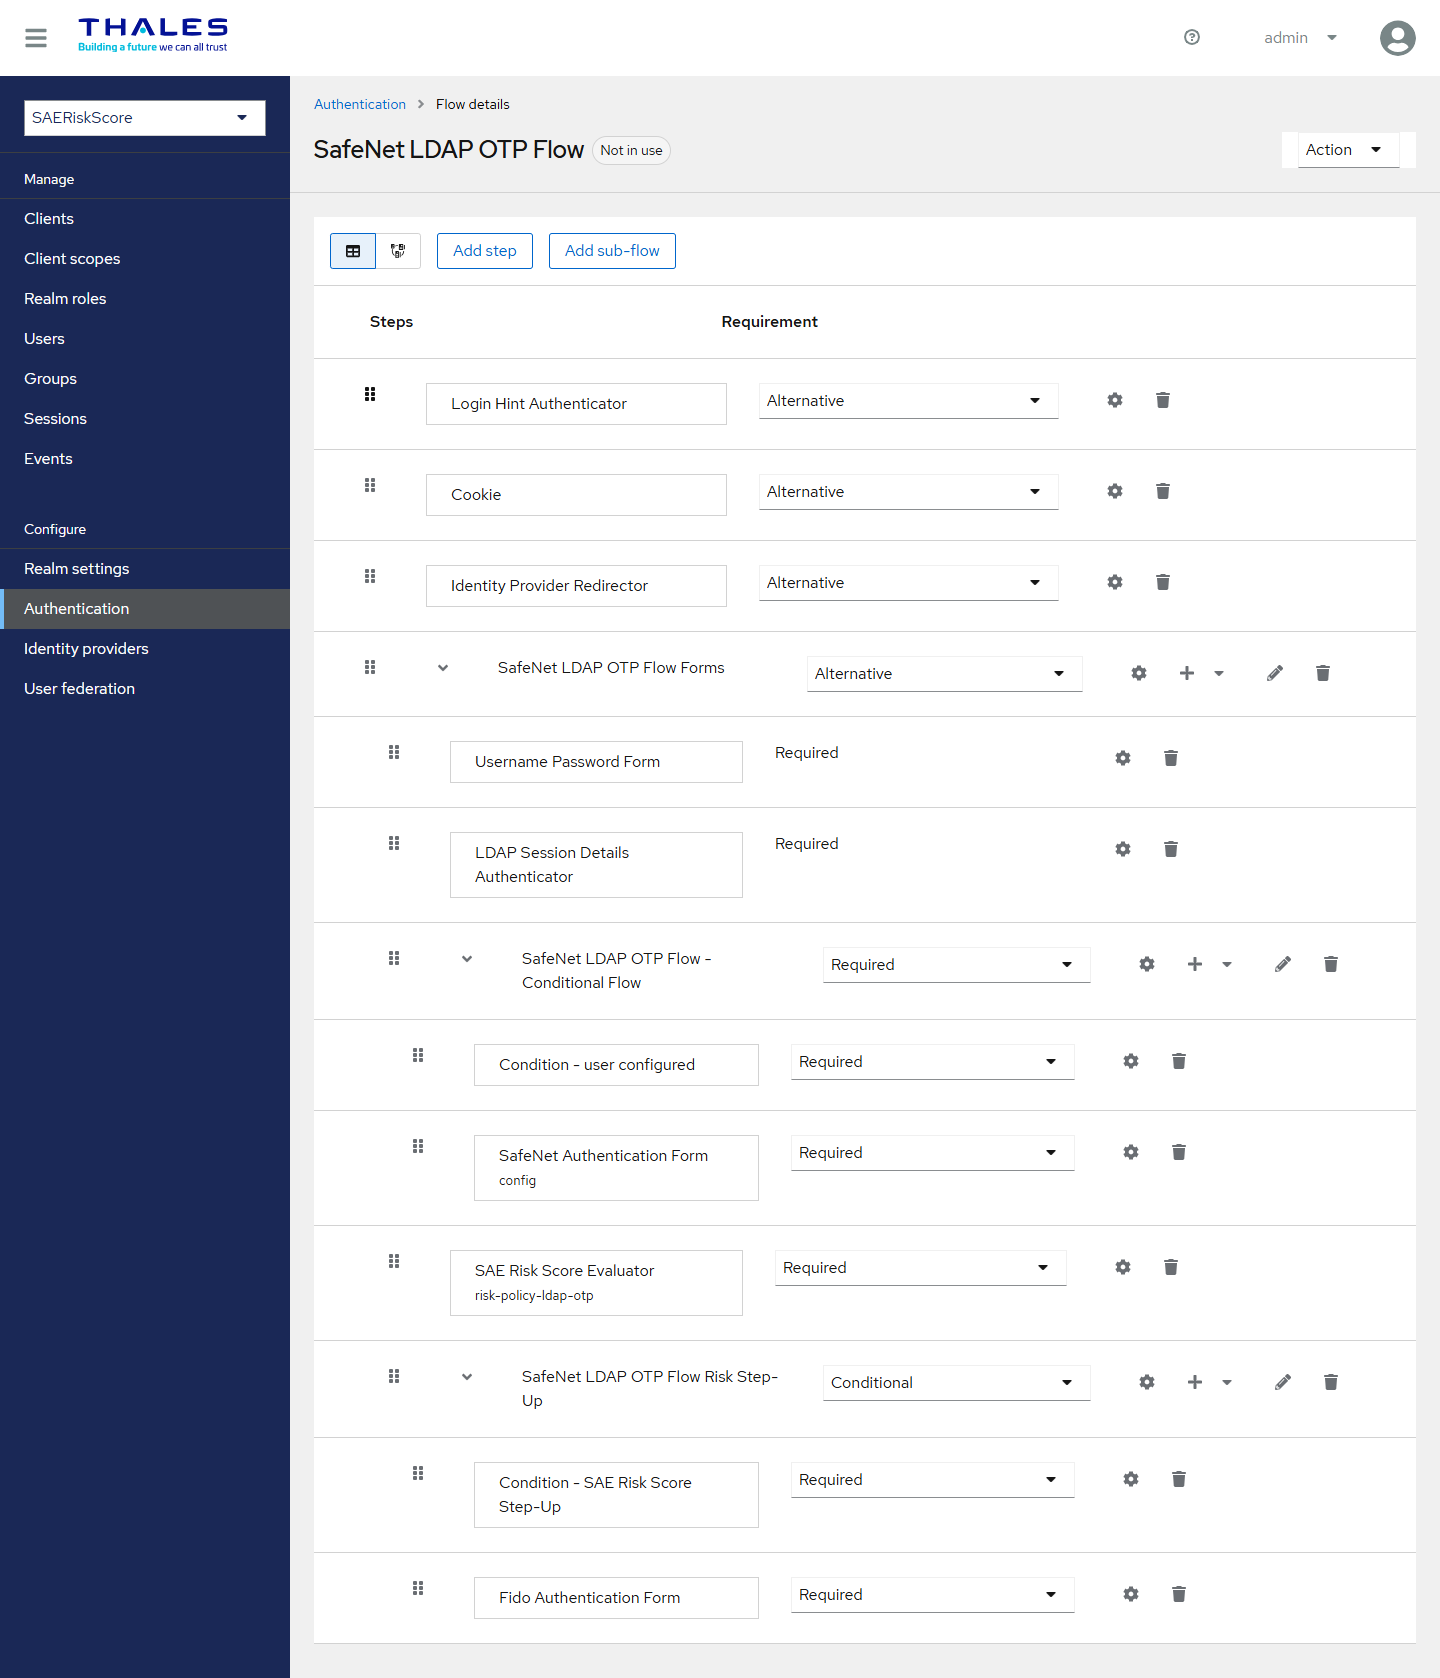
SafeNet OTP LDAP Flow with risk score evaluation
SafeNet OTP LDAP Flow
├── Login Hint Authenticator                      Alternative
├── Cookie                                        Alternative
├── Identity Provider Redirector                  Alternative
└── SafeNet OTP LDAP Flow Forms                   Alternative  (sub-flow)
    ├── Username Form                             Required
    ├── SafeNet OTP LDAP Flow -Conditional Flow   Required     (sub-flow)
    │   ├── Condition - user configured           Required
    │   └── SafeNet Authentication Form           Required
    ├── Username Password Form                    Required
    ├── LDAP Session Details Authenticator        Required
    ├── SAE Risk Score Evaluator                  Required
    └── SafeNet OTP LDAP Flow Risk Step-Up        Conditional  (sub-flow)
        ├── Condition - SAE Risk Score Step-Up    Required
        └── FIDO Authentication Form              Required
SafeNet LDAP FIDO Flow with risk score evaluation
SafeNet LDAP FIDO Flow
├── Login Hint Authenticator                      Alternative
├── Cookie                                        Alternative
├── Identity Provider Redirector                  Alternative
└── SafeNet LDAP FIDO Flow Forms                  Alternative  (sub-flow)
    ├── Username Password Form                    Required
    ├── LDAP Session Details Authenticator        Required
    ├── SafeNet LDAP FIDO Flow -Conditional Flow  Required     (sub-flow)
    │   ├── Condition - user configured           Required
    │   └── FIDO Authentication Form              Required
    ├── SAE Risk Score Evaluator                  Required
    └── SafeNet LDAP FIDO Flow Risk Step-Up       Conditional  (sub-flow)
        ├── Condition - SAE Risk Score Step-Up    Required
        └── SafeNet Authentication Form           Required
SafeNet OTP FIDO Flow with risk score evaluation
SafeNet OTP FIDO Flow
├── Login Hint Authenticator                      Alternative
├── Cookie                                        Alternative
├── Identity Provider Redirector                  Alternative
└── SafeNet OTP FIDO Flow Forms                   Alternative  (sub-flow)
    ├── Username Form                             Required
    ├── SafeNet OTP FIDO Flow -Conditional Flow   Required     (sub-flow)
    │   ├── Condition - user configured           Required
    │   ├── SafeNet Authentication Form           Required
    │   └── FIDO Authentication Form              Required
    ├── SAE Risk Score Evaluator                  Required
    └── SafeNet OTP FIDO Flow Risk Step-Up        Conditional  (sub-flow)
        ├── Condition - SAE Risk Score Step-Up    Required
        └── Password Form                         Required
In each flow, configure every SafeNet Authentication Form and FIDO Authentication Form step with the same settings as in the SafeNet flows: Agent BSID key, Token Validator URL, and the optional settings.
With the evaluator inside the Forms sub-flow, the risk score is evaluated when the user signs in with the form, but not when the user accesses another application through an existing SSO session. To evaluate the risk score on every application access, see RiskScore flow with SSO re-evaluation.
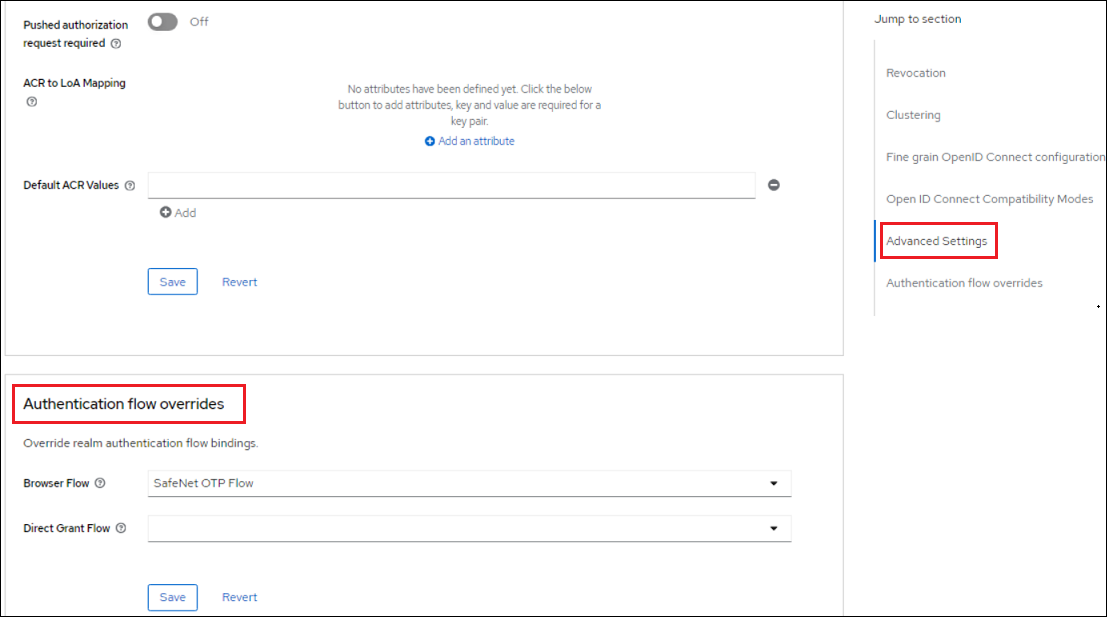
Authentication flow overrides
Authentication flow is overridden at the Client level.
Multi-tenant support
To achieve multi-tenancy in SafeNet Access Exchange, you need to create different realms. Within Multi-tenant support, you can enable user authentication with different SAS tenants. You can perform the same steps as defined above for realm creation for the new tenant and define the configuration details for the Virtual Server respective to SAS.
For each Virtual Server, different Agent BSID Key and Token Validator URL has to be provided.

